For CISOs, CROs and resilience leaders
Know your risk. Act with evidence.
The costliest incidents now arrive through suppliers, exposed systems, help desks and AI trusted too far. RiskAct shows which of those risks fit your organisation, prepares the people who must decide, and keeps a record your board, auditors and regulators can check.
Nothing to install and nothing connected to your systems. Works beside your SIEM, EDR and GRC tools.
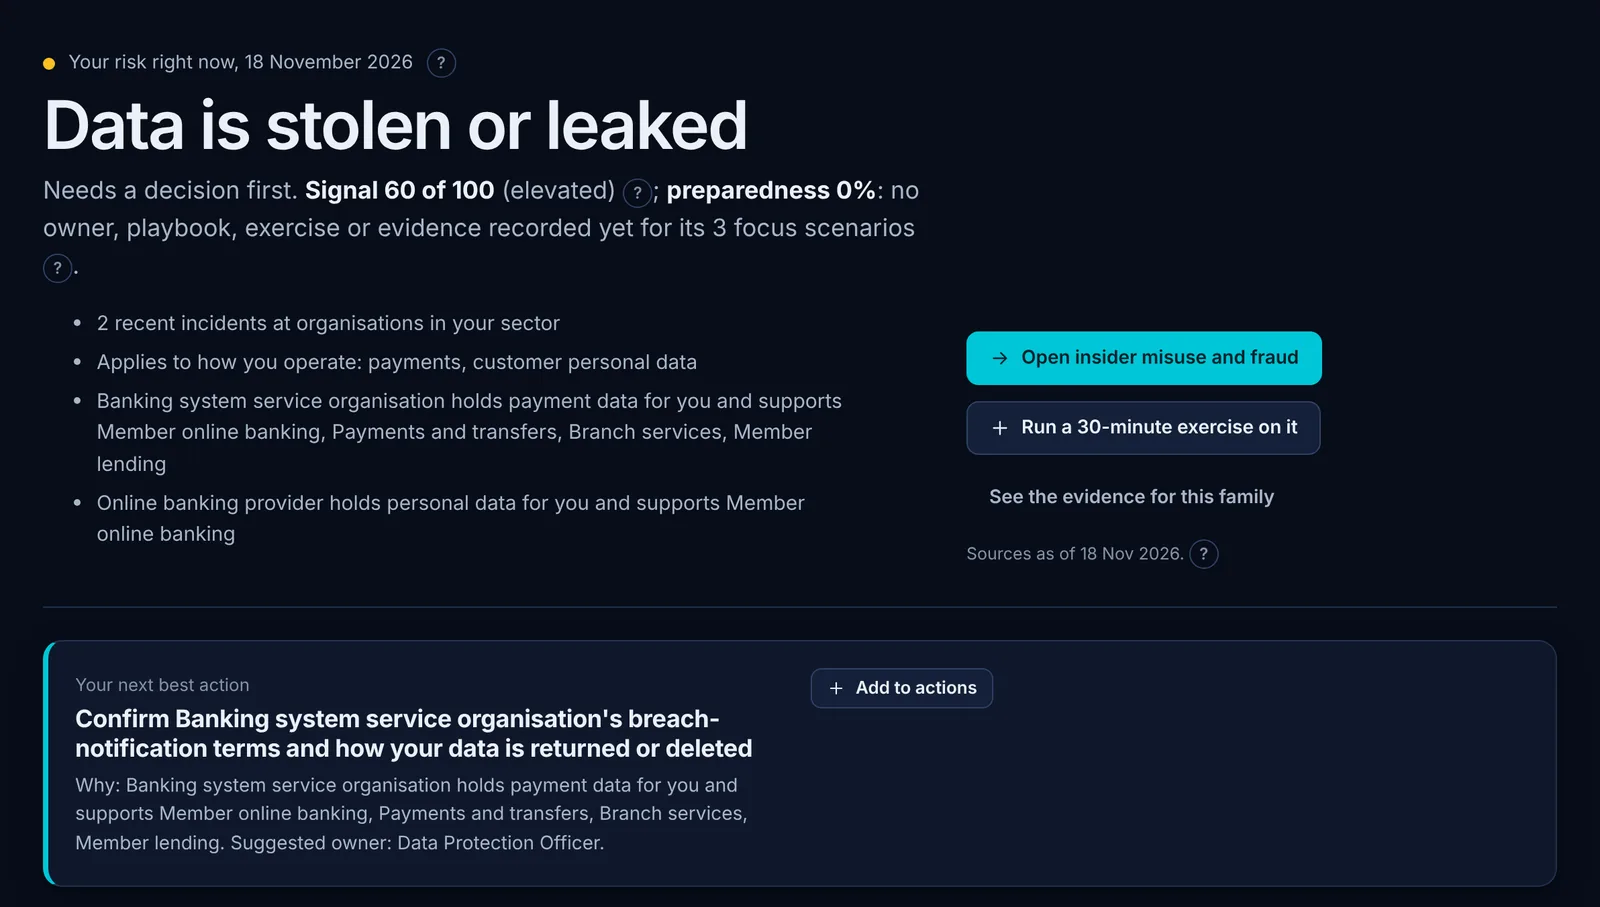
Why boards are asking
The latest industry reports point at the same places: the suppliers you rely on, the systems you expose and the AI you adopt.
- $4.99M
- Record global average cost of a data breach, up 12% in a year.IBM, Cost of a Data Breach Report 2026
- 48%
- Of breaches involved a third party, a 60% jump in a year.Verizon, 2026 Data Breach Investigations Report
- 31%
- Of breaches started with an exploited vulnerability, now the leading way in.Verizon, 2026 Data Breach Investigations Report
- 92%
- Of organisations with an AI-related breach lacked proper AI access controls.IBM, Cost of a Data Breach Report 2026
How RiskAct works
Four steps, in the order your team works through them. Each one makes the next sharper.
1Know
See which risks fit you, and why
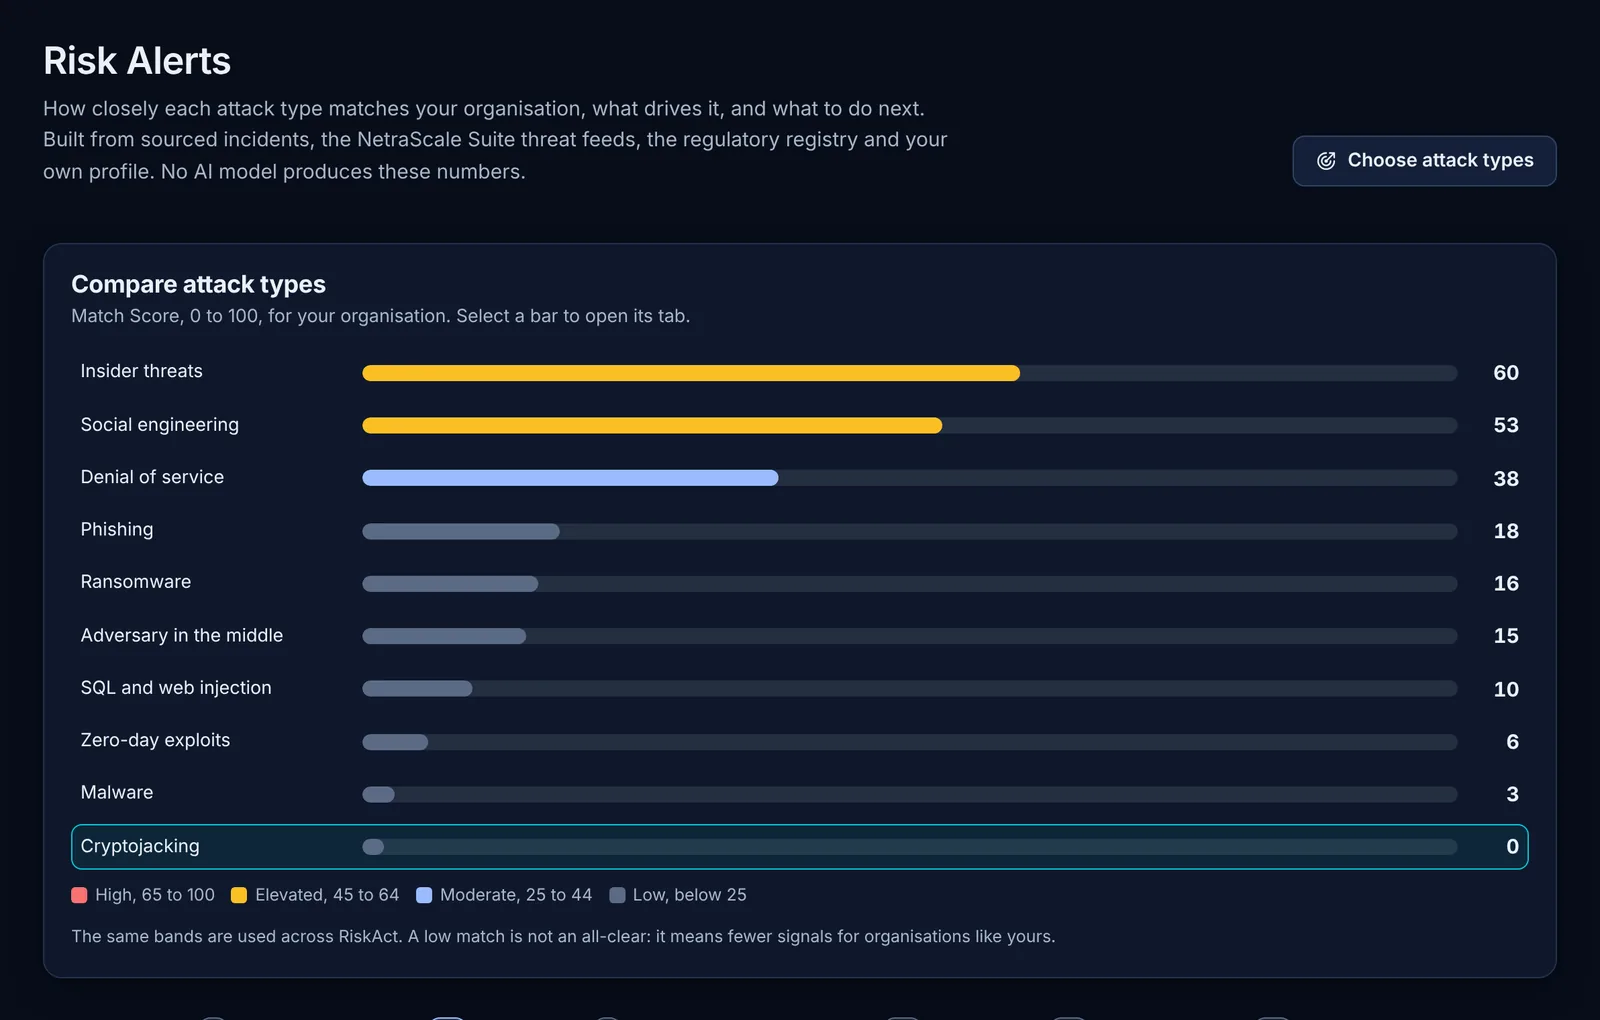
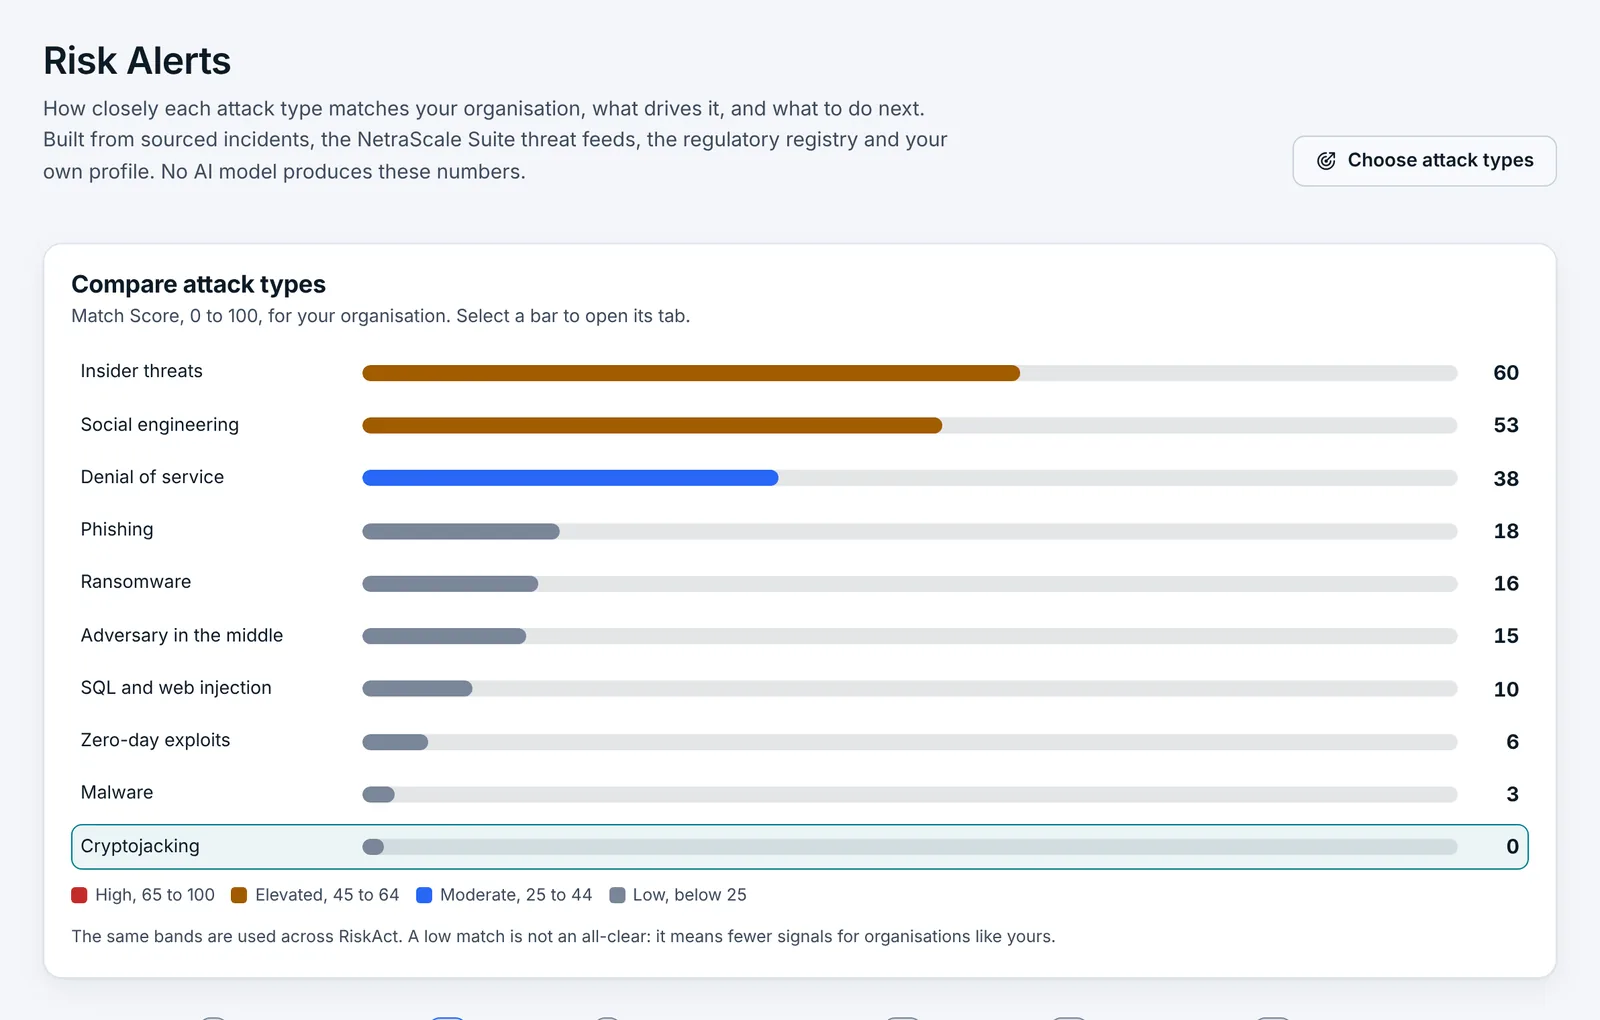
Answer a short profile. RiskAct matches you against recent, sourced incidents at similar organisations, the NetraScale Suite threat feeds and the regulations for your jurisdictions, then shows which risk needs a decision first.
- Seven plain-language risk families, from people being tricked to AI going wrong
- A Match Score for each attack type, with every point and its source shown
- News from official bodies, matched to the risks you track
2Prepare
Find the single points of failure
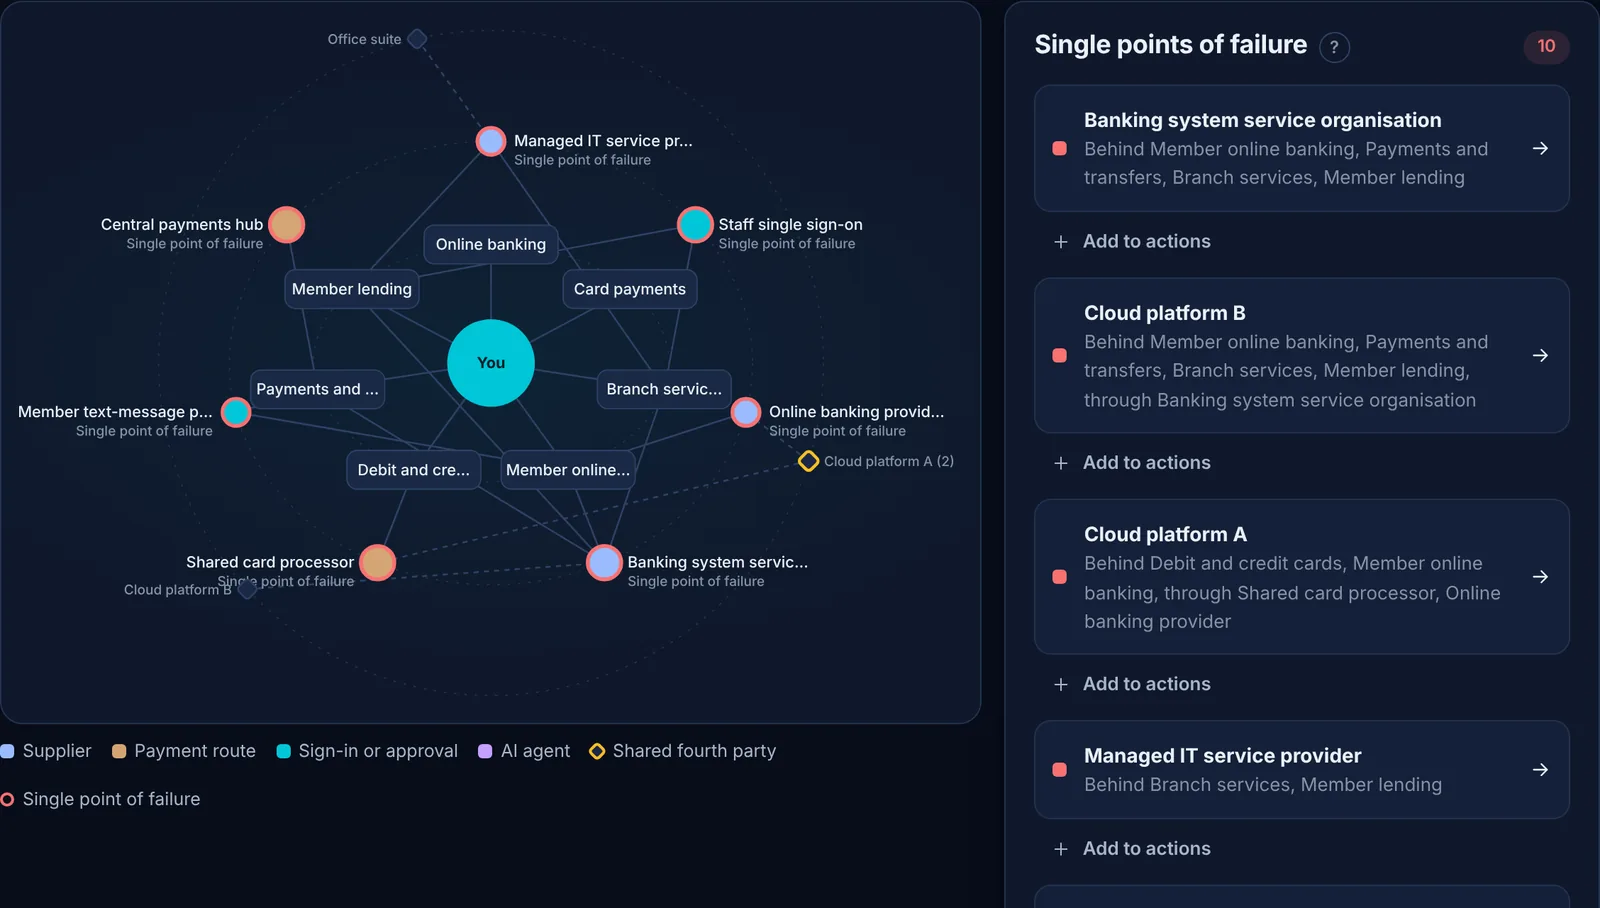
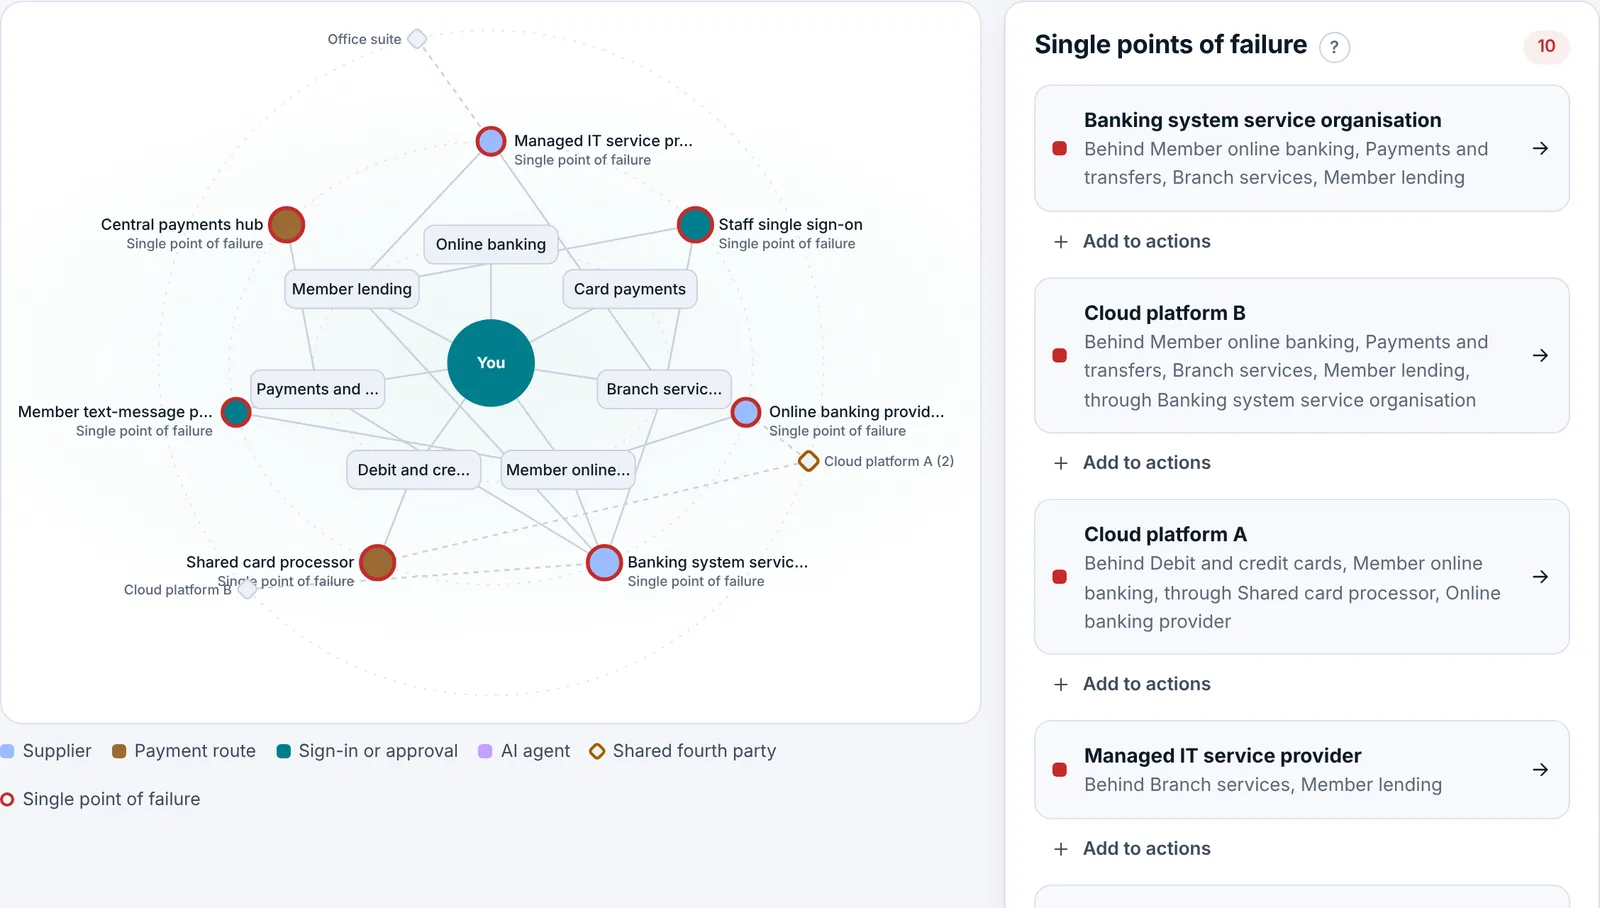
Record the suppliers, payment routes, sign-in methods and AI agents behind your critical services, or start from an example for your sector. RiskAct shows which providers sit behind several services and what stops if one fails.
- Sector examples for banks, credit unions, payments, insurance, energy, healthcare and more
- Fourth parties too: two suppliers on the same cloud share its outages
- Every finding comes with a suggested action, an owner role and a due date
3Decide
Rehearse the decisions before you need them
Run a 30-minute exercise written from your own services and suppliers, or open a real incident in the Decision Room. Your team weighs explanations, watches reporting deadlines worked out from your own timestamps, and logs every decision.
- Reporting clocks for rules such as GDPR's 72 hours, labelled until verified
- An append-only decision log: any change or removal shows
- An evidence pack with a fingerprint anyone can recompute
Decision log, exercise on a payment processor outage
- Aware of the outage; reporting clocks start from this time
- Cause weighed: supplier failure more likely than an attack
- Switch card payments to the alternative route
- Notify the regulator before the deadline; counsel to confirm
Each entry is chained to the one before it.
4Prove
Show your board, auditors and insurers
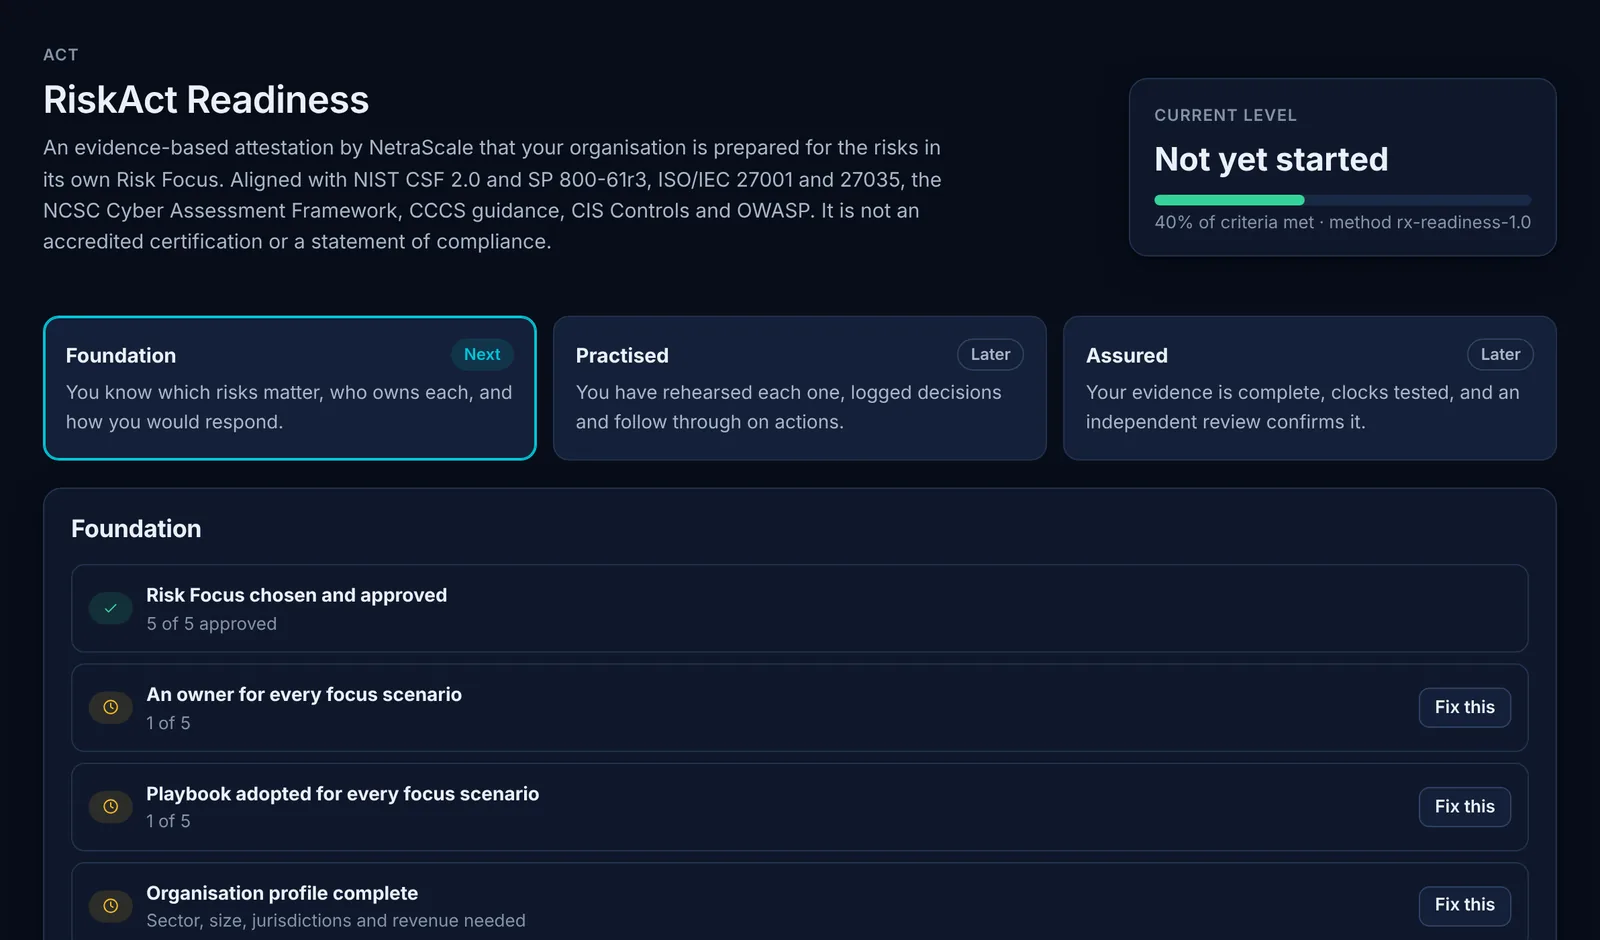
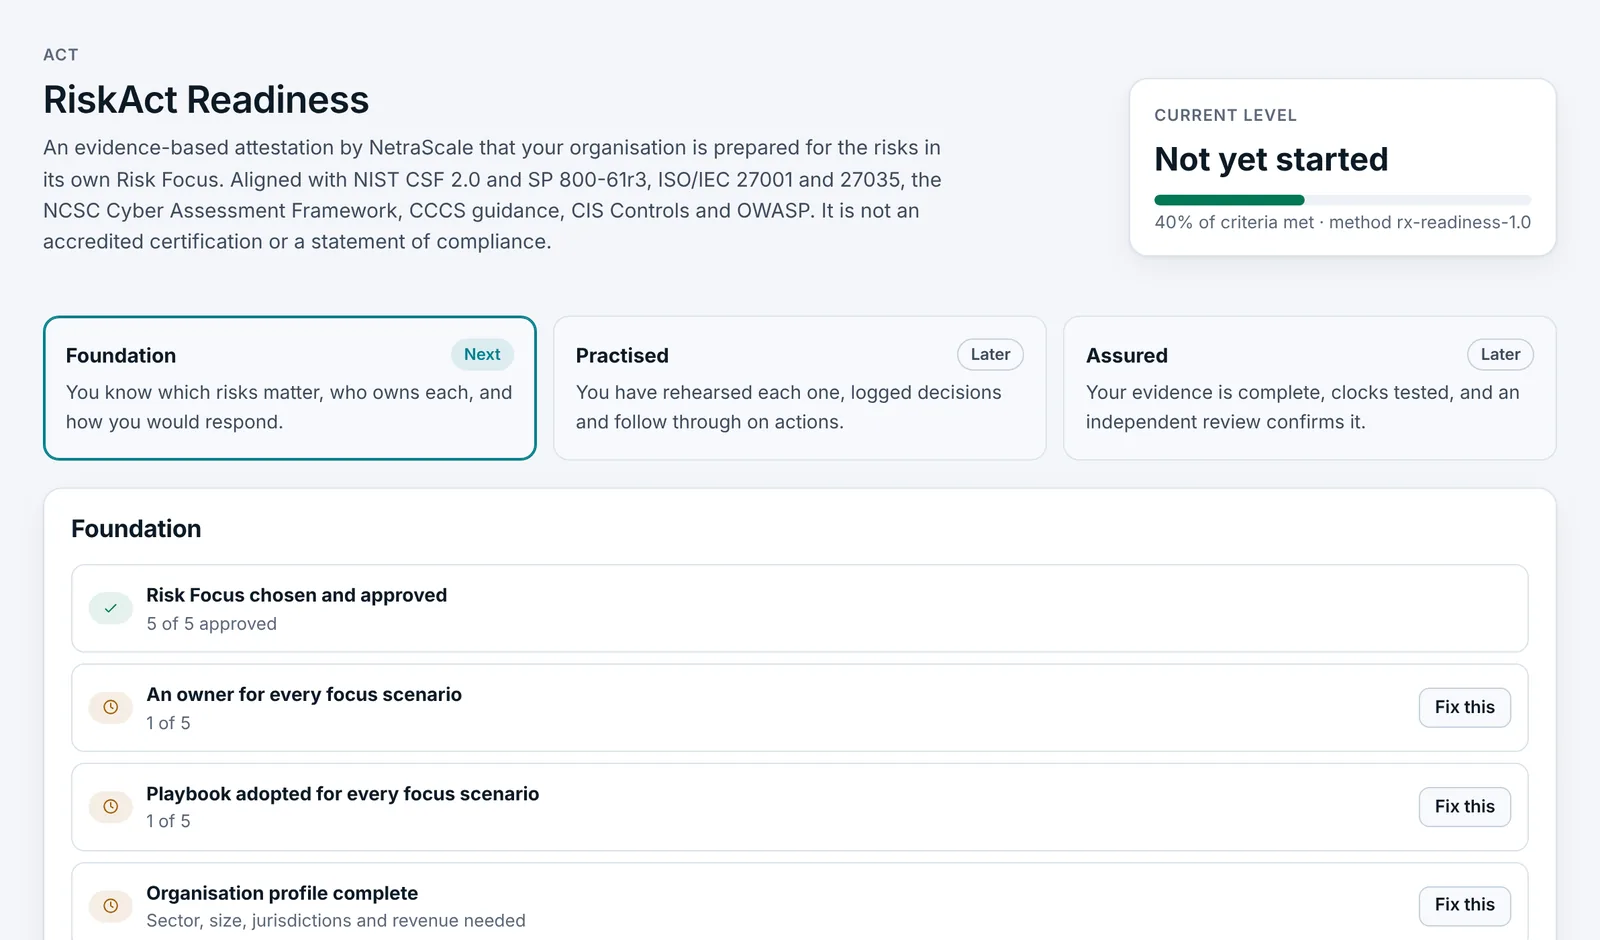
RiskAct Readiness turns the work into three levels, Foundation, Practised and Assured, each with the evidence it needs and what is still missing.
- Aligned with NIST CSF 2.0, ISO/IEC 27001 and 27035, the NCSC CAF and CCCS guidance
- Assured needs an independent review of your evidence
- An attestation by NetraScale, not an accredited certification
Built for the people who must decide
- CISOs
- A defensible view of which threats fit the organisation, tied to playbooks, owners and exercises, without another detection tool to run.
- CROs and risk teams
- Cyber risk in the language of the risk register: critical services, impact tolerances, concentration and evidence of preparedness.
- Resilience and third-party risk
- The suppliers and fourth parties behind each critical service, with single points of failure and exit plans in one place.
- Boards and audit committees
- A short, sourced answer to "are we prepared?", with the record to back it.
What RiskAct will never do
- Scan, monitor or connect to your systems. It works from what you record and from public, sourced data.
- Invent figures. Money comes from your own estimates; incidents and statistics come from cited sources.
- Use an AI model to produce scores. Every number can be traced to a published method.
- Make decisions for you. Detection, your data and any irreversible action stay with your people.
Aligned, not certified
RiskAct maps its risk families and playbooks to NIST CSF 2.0 and SP 800-61r3, ISO/IEC 27001 and 27035, the NCSC Cyber Assessment Framework, CCCS guidance, CIS Controls, OWASP and MITRE ATT&CK. That shows alignment. It is not a certification or a statement of compliance, and RiskAct says so wherever it matters.
Your organisation's data is visible only to its own members, with roles for admins, members and viewers, and single sign-on through your NetraScale account.
See your own risks in the first session
Pick your sector, list your critical services, and RiskAct shows where to decide first.